
Rocky 10: SELinux modes, labels and semanage
Test scope
Section titled “Test scope”In a Rocky Linux 10.2 VM (kernel 6.12.0-211.16.1.el10_2): sestatus, setenforce transitions, ls -Z, chcon, restorecon -Rv, adding and removing semanage fcontext rules, and ausearch -m avc. Log: plans/content-expansion/evidence/logs/rocky-selinux-basics.log.
The three modes
Section titled “The three modes”getenforcesestatus | head -5setenforce 0 && getenforcesetenforce 1 && getenforceEnforcingLoaded policy name: targetedCurrent mode: enforcingMode from config file: enforcingPermissiveEnforcingsetenforce only toggles Enforcing ↔ Permissive; it cannot disable SELinux. Disabled requires editing /etc/selinux/config and rebooting, and going from Disabled back to Enforcing forces a full relabel on the next boot.
Reading labels with ls -Z
Section titled “Reading labels with ls -Z”mkdir -p /srv/lab && echo hi > /srv/lab/f.txtls -Z /srv/lab/f.txtunconfined_u:object_r:var_t:s0 /srv/lab/f.txtThe format is user:role:type:level; for troubleshooting the type is what matters — var_t, httpd_sys_content_t, and so on.
chcon gets overwritten by restorecon
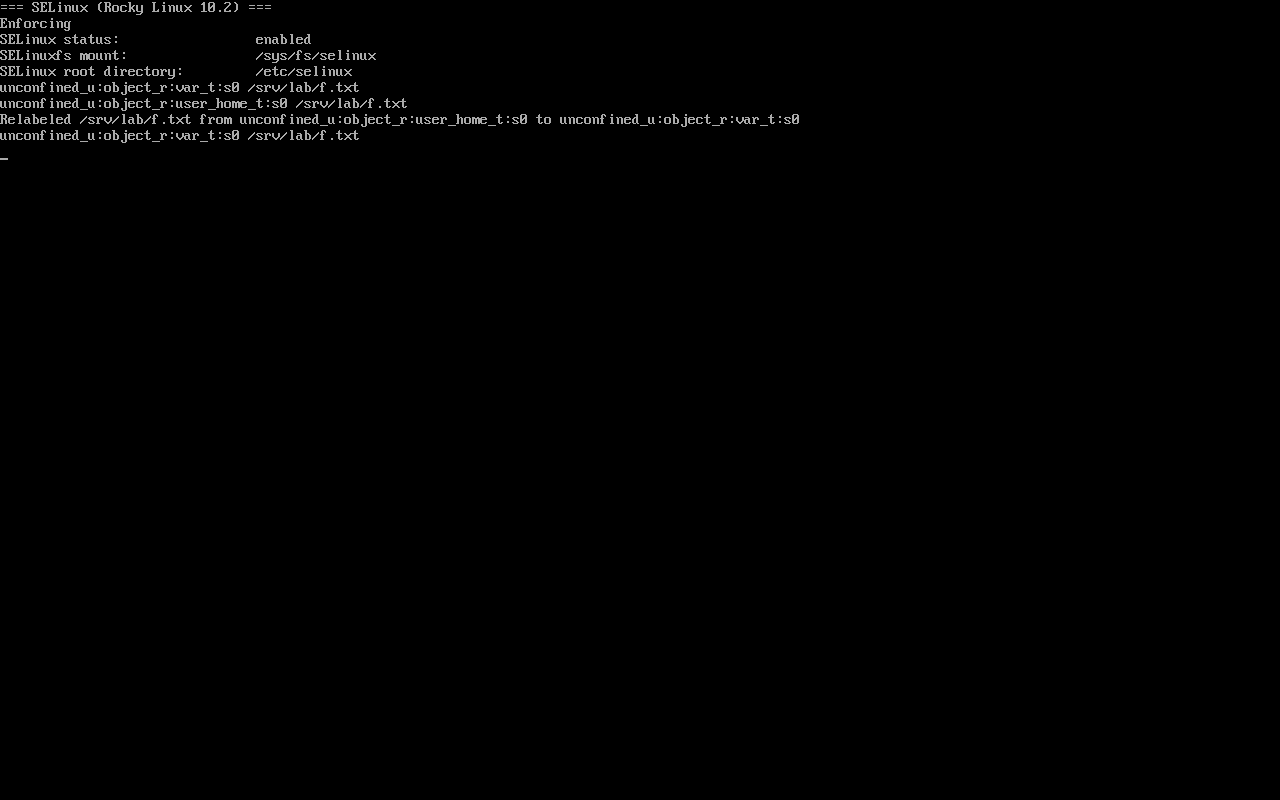
Section titled “chcon gets overwritten by restorecon”chcon -t user_home_t /srv/lab/f.txtls -Z /srv/lab/f.txtrestorecon -Rv /srv/labls -Z /srv/lab/f.txtunconfined_u:object_r:user_home_t:s0 /srv/lab/f.txtRelabeled /srv/lab/f.txt from unconfined_u:object_r:user_home_t:s0 to unconfined_u:object_r:var_t:s0unconfined_u:object_r:var_t:s0 /srv/lab/f.txtchcon changes the current label only; restorecon restores the policy default. Use chcon for temporary changes and semanage for anything persistent.
semanage: teach restorecon about your directory
Section titled “semanage: teach restorecon about your directory”semanage fcontext -a -t httpd_sys_content_t "/srv/lab(/.*)?"restorecon -Rv /srv/labls -Z /srv/lab/f.txtRelabeled /srv/lab/f.txt from unconfined_u:object_r:var_t:s0 to unconfined_u:object_r:httpd_sys_content_t:s0unconfined_u:object_r:httpd_sys_content_t:s0 /srv/lab/f.txtRemoving the rule and relabelling:
semanage fcontext -d "/srv/lab(/.*)?"restorecon -Rv /srv/labRelabeled /srv/lab from ...httpd_sys_content_t:s0 to ...var_t:s0Relabeled /srv/lab/f.txt from ...httpd_sys_content_t:s0 to ...var_t:s0Finding AVC denials
Section titled “Finding AVC denials”ausearch -m avc -ts recent<no matches>A clean system has no denials; when they appear, ausearch shows denied { ... } with scontext/tcontext/tclass, and audit2why explains the cause.
Common traps
Section titled “Common traps”- Treating chcon as permanent: a single
restoreconreverts it; - Confusing Disabled with Permissive: Disabled loads no policy at all and returning to Enforcing requires a relabel;
- semanage not found: it ships in
policycoreutils-python-utils, which minimal and cloud images may omit.
Practice: add a custom context and remove it
Section titled “Practice: add a custom context and remove it”sudo dnf install -y policycoreutils-python-utilssudo mkdir -p /srv/lab && echo hi | sudo tee /srv/lab/f.txtls -Z /srv/lab/f.txtsudo semanage fcontext -a -t httpd_sys_content_t "/srv/lab(/.*)?"sudo restorecon -Rv /srv/labls -Z /srv/lab/f.txtsudo semanage fcontext -d "/srv/lab(/.*)?" && sudo restorecon -Rv /srv/labls -Z /srv/lab/f.txtChecks:
- The initial type is
var_t - After semanage plus restorecon it becomes
httpd_sys_content_t - Deleting the rule returns it to
var_t sestatusstill reports enforcing
常见问题
Can setenforce 0 replace disabling SELinux?
It only switches to permissive (log but do not deny). Full disable requires /etc/selinux/config and a reboot; coming back from disabled to enforcing requires a relabel.
Why does my chcon change revert?
restorecon restores the policy default. Persistent changes need a semanage fcontext rule followed by restorecon.
ausearch finds no AVC — what now?
Confirm auditd is running and the time range covers the failure (-ts recent or -ts today); containers usually have no auditd, so host AVCs are invisible there.
Next steps
Section titled “Next steps”- Network triage: Triage network problems by symptom
- Firewall: firewalld rich rules
- Post-install checks: 7 checks after install