
Rocky 10: finding, changing and reverting SELinux booleans
Test scope
Section titled “Test scope”A Rocky Linux 10.2 Server VM with SELinux Enforcing and policycoreutils-python-utils installed.
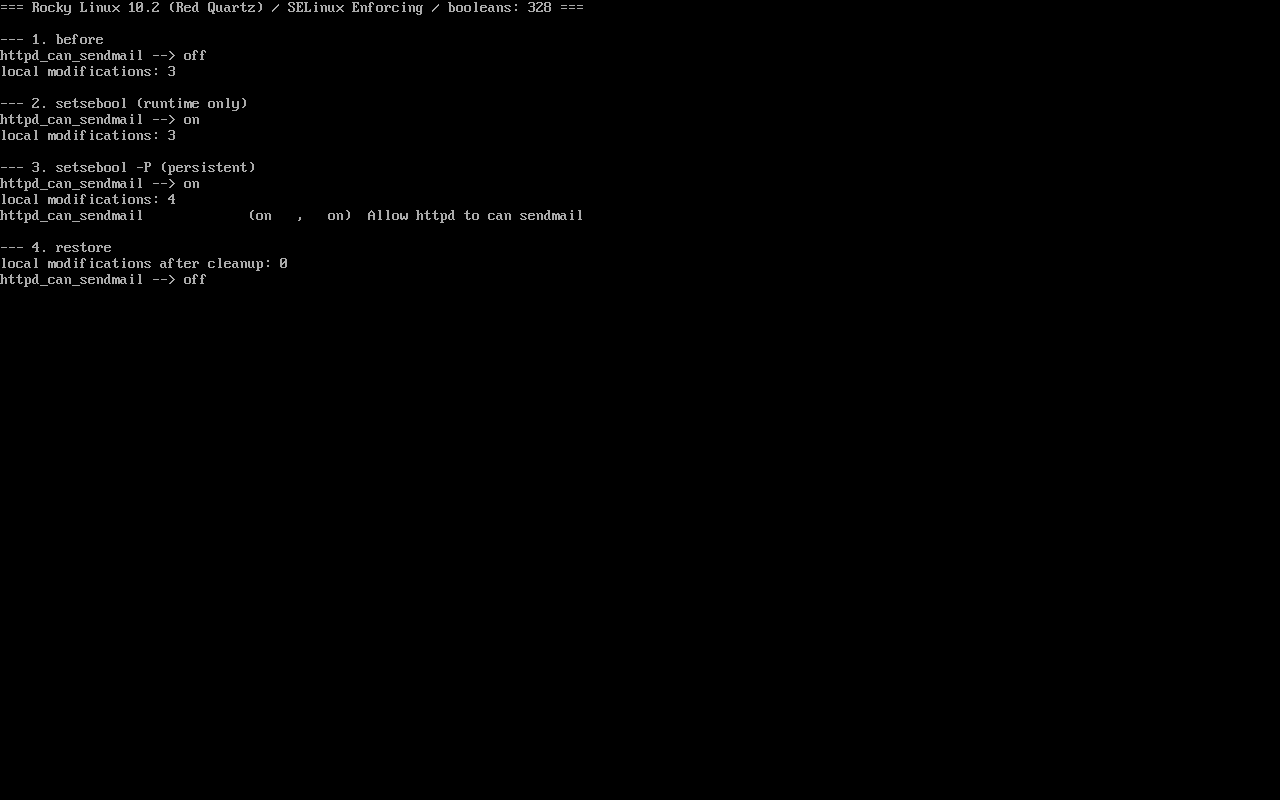
One session covered: enumeration, descriptions, runtime change, persistent change, override inspection, cleanup. Screenshot: public/evidence/selinux/rocky-booleans.png.
Three commands for discovery
Section titled “Three commands for discovery”$ getsebool -a | wc -l328$ getsebool httpd_can_sendmailhttpd_can_sendmail --> off$ semanage boolean -l | grep -E "^httpd_can_sendmail "httpd_can_sendmail (off , off) Allow httpd to can sendmailgetsebool -afor bulk values in scripts;getsebool <name>to confirm one;semanage boolean -lfor descriptions and defaults.
To find switches for a service, grep by name:
$ semanage boolean -l | grep -i -E "nfs|samba" | head -5Changing: two lifetimes
Section titled “Changing: two lifetimes”$ setsebool httpd_can_sendmail on # runtime only$ semanage boolean -l -C | tail -n +2 | wc -l0$ setsebool -P httpd_can_sendmail on # written to the policy store$ semanage boolean -l -C | tail -n +2 | wc -l2semanage boolean -l -C lists local customizations only, which makes it the reliable way to tell whether a change will survive a reboot.
Storage location
Section titled “Storage location”$ ls /var/lib/selinux/targeted/active/booleans.local/var/lib/selinux/targeted/active/booleans.localOlder documentation points at /etc/selinux/targeted/active/; that path no longer exists in the modern store.
Triage order: AVC first, boolean last
Section titled “Triage order: AVC first, boolean last”1) ausearch -m AVC -ts recent # is anything denied, and what2) audit2why < /var/log/audit/audit.log | tail -203) ls -Z <file> / restorecon -Rv <dir> # fix labels first4) labels correct but still blocked -> now consider a booleanReversed order wastes time: booleans only toggle rules already present in the policy and cannot repair a wrong label.
Reverting
Section titled “Reverting”$ setsebool -P httpd_can_sendmail off # single item (override remains)$ semanage boolean -D # clear all overrides$ semanage boolean -l -C | tail -n +2 | wc -l0-D is global; on shared machines list the current overrides before running it.
Common traps
Section titled “Common traps”- Changing a boolean without restarting the service: some services read policy once at start;
- Expecting a boolean to open a port: reachability is firewalld’s job;
- Using
-Dto “delete one entry”: it removes all; - Looking for
sesearchon a default install: it needssetools-console.
Practice: a complete round trip
Section titled “Practice: a complete round trip”sudo semanage boolean -l -C | tail -n +2 | wc -l # record the baselinesudo getsebool httpd_can_sendmailsudo setsebool httpd_can_sendmail onsudo semanage boolean -l -C | tail -n +2 | wc -l # still baselinesudo setsebool -P httpd_can_sendmail onsudo semanage boolean -l -C | tail -n +2 | wc -l # baseline + 1sudo setsebool -P httpd_can_sendmail offsudo semanage boolean -Dsudo semanage boolean -l -C | tail -n +2 | wc -l # 0Checks:
- Only
-Pincreases the count; -Dbrings it back to zero and booleans to policy defaults;- No service was disturbed;
- The baseline was recorded for rollback.
常见问题
Can I create custom booleans?
Yes, by declaring gen_bool in your own policy module — that is policy development rather than an operations switch.
Why is semanage missing?
It ships in policycoreutils-python-utils, which minimal images omit; the Server environment includes it.
How do I undo a bad boolean quickly?
Set it back with setsebool -P, or clear all overrides with semanage boolean -D and re-verify each one.
Next steps
Section titled “Next steps”- Labels and contexts: /en/selinux-basics/
- Hardening: /en/security-baseline/
- Logs: /en/journald-logging/